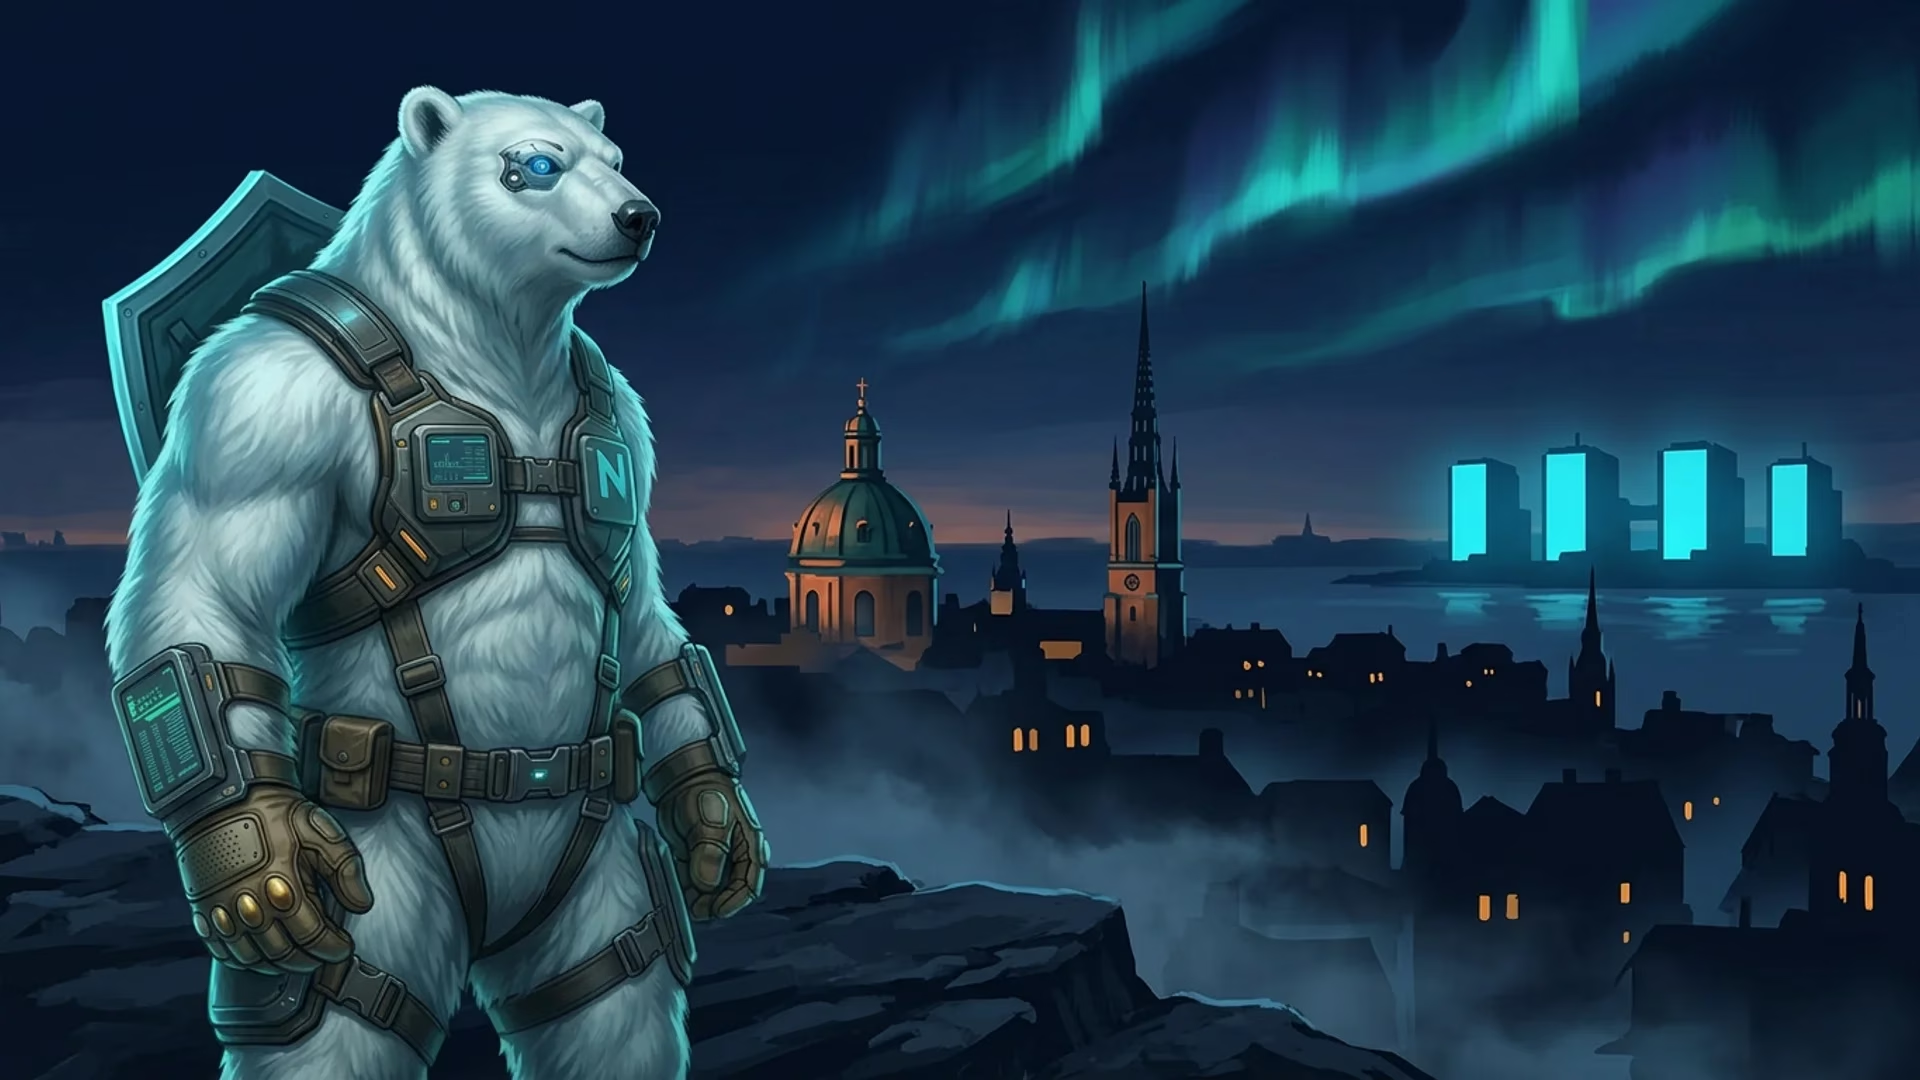
Editorial composition: a Swedish constitutional press-freedom heritage scene — a bound 1766 Tryckfrihetsförordningen volume on a granite plinth in the foreground, the Stockholm Old-Town silhouette in soft aurora light behind, the NordBastion polar-bear mascot standing watch on a wharf
Jurisdiction · Sweden · Constitutional deep-dive

Sweden.
Press freedom as constitutional law, source secrecy as criminal statute.

A deep read of the regime that reaches a server in Stockholm: Tryckfrihetsförordningen (1766), Yttrandefrihetsgrundlagen (1991), TF Chapter 3 source protection, IMY enforcement — and the parts where the shield runs out.

TL;DR
  • 01

    Tryckfrihetsförordningen (1766, last revised 2018) and Yttrandefrihetsgrundlagen (1991) are constitutional acts that rank above ordinary statute.

  • 02

    TF Chapter 3 makes it a criminal offence to disclose an anonymous source, and forbids public authorities from even investigating who one is.

  • 03

    Honest limits: EU member, EU e-Evidence regulation lands in full 2026, SÄPO cooperates with allied signals-intelligence services.

The regime

Four constitutional acts, two of them about expression. Older than the United States.

The Kingdom of Sweden has four grundlagar — constitutional acts that rank above ordinary statute and can only be amended by two consecutive Riksdag votes with an intervening general election. They are the Instrument of Government (Regeringsformen), the Act of Succession, the Freedom of the Press Act (Tryckfrihetsförordningen, TF, 1766, last comprehensive revision 2018) and the Fundamental Law on Freedom of Expression (Yttrandefrihetsgrundlagen, YGL, 1991). The last two are the ones a hosting provider lives under.

TF is the older document — older than the United States Constitution, older than the French Revolution, older than the Bill of Rights. It was enacted on 2 December 1766 under King Adolf Frederick and codified, for the first time in any continuously functioning legal system, freedom of the press as a positive right. The 2018 revision modernised the language and expanded the scope to cover modern printing and distribution; it did not weaken the core guarantees. YGL was added in 1991 to extend the same regime to "technical recordings" — radio, television, video, websites — that did not exist when TF was drafted.

The clause that matters most to an infrastructure operator is källskydd — source protection — codified at TF Chapter 3. § 1 obliges anyone who receives information for publication to protect the source's identity. § 3 forbids disclosure without consent, except in narrow enumerated cases (typically grave crimes against the realm, listed exhaustively). § 4 prohibits public authorities from investigating who a source was. § 5 makes unauthorised disclosure a criminal offence punishable by fine or imprisonment. The combined effect is rare in European law: the operator is criminally liable for breaking source secrecy, and the state is criminally constrained from even asking.

YGL extends the same architecture to electronic publication. The strongest tier of YGL protection — formal designation as a publication with a responsible publisher (ansvarig utgivare) and an utgivningsbevis issued by the Myndigheten för press, radio och tv — is opt-in. Sites without a certificate still benefit from baseline YGL principles and from general European press-freedom case law, but the certificated regime is the most explicit shield available on the open market. NordBastion does not file utgivningsbevis on behalf of customers; this is a project-level decision the customer makes in their own name when it fits.

Three readings

Regulator, precedent, limits. All three matter.

Constitutional text is only half the answer. The other half is who enforces it, who has tested it, and where it runs out.

The regulator · IMY

Integritetsskyddsmyndigheten

IMY is the Swedish data-protection authority and one of the more assertive GDPR regulators in the EU. Documented enforcement against Swedish public bodies for unlawful Google Analytics transfers (2023), credit-reference agencies for excessive retention, and a string of decisions narrowing school facial-recognition pilots.

For a customer this cuts both ways: IMY backs your Article 17 erasure rights with real penalties, and constrains NordBastion — by external regulator — to the Article 5 minimisation we ship under by choice.

The precedent · Pionen 2010–2018

Bahnhof, WikiLeaks, the bunker

From the 2010 diplomatic-cable releases through 2018, Bahnhof — operating from the Pionen bunker in central Stockholm — kept WikiLeaks public-facing infrastructure online through eight years of allied diplomatic pressure. No Swedish court ordered disclosure of source material; no Swedish court ordered takedown.

NordBastion does not run inside Pionen — STO.001 is in a different tier-III facility in the metropolitan area. The regime that protected Bahnhof and WikiLeaks then is the regime that reaches a NordBastion bastion now.

The limits · honestly

EU membership, e-Evidence, SÄPO

Sweden has been an EU Member State since 1995. EU e-Evidence (Regulation 2023/1543) enters full application in 2026, creating direct European Production and Preservation Orders. Säkerhetspolisen cooperates with US, UK and other allied signals-intelligence services under documented arrangements.

None of this nullifies TF/YGL — constitutional acts still rank above ordinary statute — but they are the points where the shield runs out, and you should know about them before you place a workload here.

Verdict

Pick Sweden when the workload needs a written constitutional shield with criminal-statute source secrecy.

Sweden is the right answer when the workload is publishing — a news site, a media archive, a leak intake, a publication infrastructure that needs the most explicit press-freedom guarantee currently available on the open hosting market. TF and YGL are not policy promises. They are constitutional acts older than the United States, with source secrecy enforced by criminal statute.

It is not the right answer for every workload. If your model treats EU jurisdiction itself as the threat, Iceland (outside the EU and EEA from this angle) or Norway (EEA without e-Evidence) is the better fit. If your priority is signals-intelligence resistance, no hosting jurisdiction substitutes for application-layer encryption — and that is true everywhere, not just Sweden.

What Sweden gives you that nowhere else does: a 260-year-old constitutional regime, source secrecy as criminal offence, an assertive regulator backing your erasure rights, and a documented eight-year precedent (Bahnhof / WikiLeaks 2010–2018) of the regime actually holding under pressure.

FAQ · Swedish law

Constitution, statute, case law.

Specific questions about the Swedish constitutional regime, source secrecy, IMY enforcement and the EU-membership trade-offs.

Is Tryckfrihetsförordningen really a constitution?

Yes — in the strict Swedish sense. The Kingdom of Sweden has four constitutional acts (grundlagar): the Instrument of Government (Regeringsformen), the Act of Succession, Tryckfrihetsförordningen (TF, 1766, last comprehensive revision 2018) and Yttrandefrihetsgrundlagen (YGL, 1991). Together they rank above ordinary statute and can only be amended by two consecutive Riksdag votes with an intervening general election. TF and YGL are the two that matter for a hosting provider — they encode press freedom, source secrecy and the prohibition on prior restraint as constitutional rights, not statutory grants.

What does TF Chapter 3 actually say about sources?

TF Chapter 3 § 1 codifies källskydd — source protection — as a positive duty on anyone who receives information for publication. § 3 forbids the recipient from disclosing the source's identity without consent, except in narrow enumerated cases (typically grave crimes against the realm). § 5 makes such unauthorised disclosure a criminal offence punishable by fine or imprisonment. § 4 separately prohibits public authorities from investigating who a source was. The combined effect is rare in European law: the operator is criminally liable for breaking source secrecy, and the state is criminally constrained from even asking.

Does YGL extend the same shield to a website or VPS?

Yes, with a procedural step. YGL extends TF-grade protection to "technical recordings" and electronic publications, including websites — but the strongest tier (a formal utgivningsbevis, a publication certificate issued by the Myndigheten för press, radio och tv) requires a designated responsible publisher and an application. Sites without a certificate still benefit from baseline YGL principles and from general European press-freedom case law, but the certificated regime is the strongest available. NordBastion does not issue certificates for customer workloads; the customer applies in their own name where it makes sense for the project.

How assertive is IMY in practice?

Integritetsskyddsmyndigheten (IMY) is among the more active GDPR regulators in the EU. Recent enforcement includes fines against Swedish public-sector bodies for unlawful Google Analytics transfers (2023), against credit-reference agencies for excessive retention, and a series of targeted investigations into school facial-recognition pilots. For a hosting customer this matters in two directions: IMY backs your Article 17 erasure rights with real penalties, and it constrains NordBastion — by external regulator, not just internal policy — to the Article 5 minimisation that we ship under by choice.

What is the Pionen / WikiLeaks precedent and how is it relevant?

From 2010 onwards Bahnhof, operating from the Pionen bunker in Stockholm, hosted WikiLeaks through the diplomatic-cable releases and continued to host the organisation's public-facing infrastructure into 2018. Throughout that window — under significant US and allied diplomatic pressure — the Swedish constitutional regime kept the infrastructure online. No Swedish court ordered Bahnhof to disclose source material or to take down the site. NordBastion does not run inside Pionen — STO.001 is in a different tier-III facility in the Stockholm metropolitan area — but the legal regime that protected Bahnhof and WikiLeaks then is the legal regime that reaches a NordBastion bastion now.

What about the EU e-Evidence regulation?

This is the honest weak spot. The EU's e-Evidence package (Regulation (EU) 2023/1543 and the accompanying directive) creates European Production Orders and European Preservation Orders that a competent authority in one Member State can serve directly on a service provider in another, with comparatively short response windows. It enters full application in 2026. Sweden is in scope as an EU Member State. Two structural points mitigate but do not eliminate the exposure: (a) e-Evidence still requires a valid order from a judicial or equivalent authority on a named subject for specified data, not bulk; (b) NordBastion does not collect identity, does not retain payment-card data and rotates infrastructure logs aggressively — orders intersect only with the narrow set we actually hold, which is published in the transparency report.

Does SÄPO cooperation undermine all of this?

Säkerhetspolisen (SÄPO) is Sweden's domestic security service and is a documented participant in cooperation with US, UK and other allied intelligence services — the FRA signals-intelligence cooperation revealed in the 2013 Snowden documents is the most-cited public example. That cooperation operates at the signals-intelligence and counter-terrorism layer, not as ordinary legal process against a hosting customer, and is constrained by Swedish statute (Lag (2008:717) om signalspaning i försvarsunderrättelseverksamhet, plus parliamentary oversight by SIUN). For an ordinary hosting workload it is not the day-to-day risk; for a workload that genuinely attracts state-actor adversaries, no hosting jurisdiction on earth is a substitute for application-layer encryption and operational hygiene.

Can a Swedish court compel NordBastion to identify a customer?

Only through a Swedish court order, on a named subject, for data we actually hold — and that intersection is narrow by design. We do not collect identity at signup. We do not retain payment-card data (crypto only, with no KYC). We do not log application-level activity inside customer VMs (we cannot — we do not have access). Infrastructure logs are kept on the rotation schedule published in the transparency report. What does not exist cannot be compelled. What does exist is answered to the minimum we are genuinely required to disclose, and the aggregate of those answers is published monthly.

Is the Tele2 Sverige judgment still good law?

Yes. Tele2 Sverige AB v. Post- och telestyrelsen (CJEU C-203/15, 2016) struck down the Swedish blanket data-retention regime as incompatible with EU fundamental rights. The replacement statute — Lag (2003:389) om elektronisk kommunikation, as amended — is much narrower and targeted, and applies to providers of electronic communications networks (telcos), not to hosting providers. NordBastion is not subject to bulk retention obligations under that regime. Subsequent CJEU decisions (La Quadrature du Net, 2020; SpaceNet, 2022) have reaffirmed the principle.

Private hosting, built in the North.